❌

Reading view

AI-powered cyberattacks fuel 'Black October' fears

Startup founder Colin Parsons woke up to roughly 50 billing notifications he never expected. He reported that his OpenAI and Anthropic accounts had racked up $449 in charges he didn't recognize. It was an expensive surprise that highlights how quickly stolen credentials can become a financial headache.

His experience comes as hackers increasingly use artificial intelligence to automate attacks at speeds that leave security teams scrambling. Meanwhile, researchers have uncovered dangerous weaknesses in software that helps power millions of websites.

Some cybersecurity professionals are calling this turbulent period "Black October." The name may sound dramatic, but the developments behind it deserve attention. And while many attacks target large organizations, the consequences can eventually reach your personal accounts. Here's what's happening, how AI-powered cyberattacks are changing online security and what you can do to protect yourself.

Join our upcoming CyberGuy LIVE class: 5 Ways to Travel Smarter and Save Money

In this free live online class, Kurt "CyberGuy" Knutsson will share five practical ways to protect your trip and your wallet this holiday travel season. You’ll learn how to secure your phone and personal information, find better travel deals, avoid common scams, save money on bookings and use technology to make your travels easier and less stressful. No technical experience is needed.

Join us Saturday, October 31, at 11 AM ET / 8 AM PT. Register free now at CyberGuyLive.com.

BILL GATES SOUNDS ALARM ON AI-POWERED CYBERATTACKS, WARNS OF 'NEGATIVE SURPRISES' WITHIN A YEAR

Why cybersecurity experts are calling it Black October

October 2026 has delivered a troubling wave of cybersecurity developments. Hackers have gained access to more powerful tools, while researchers have uncovered serious weaknesses in widely used software. Security professionals are reportedly struggling to keep pace with increasingly automated attacks. Some have started calling the current wave "Black October."

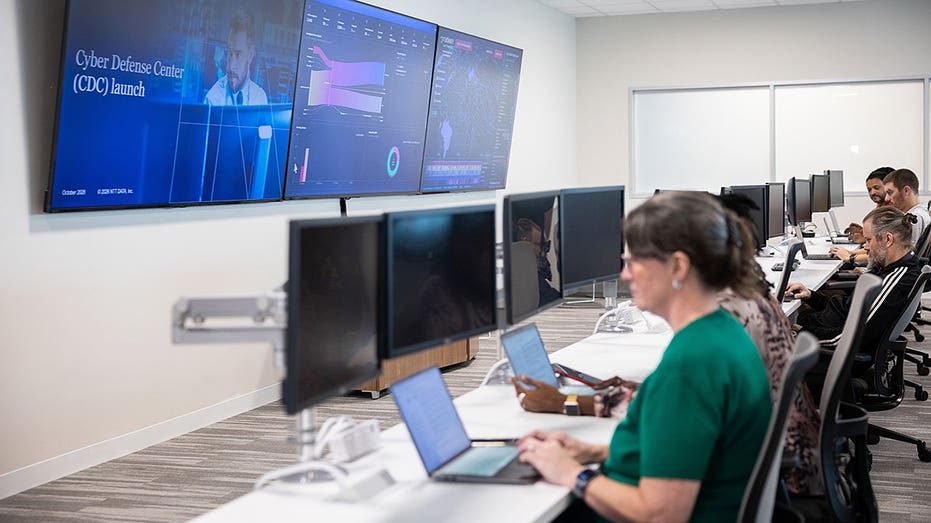
The term describes a series of cybersecurity emergencies rather than a single coordinated hacking campaign. The biggest concern is speed. Traditionally, hackers needed significant time and technical expertise to investigate potential targets. They also had to develop attack methods and analyze the information they obtained. Now, AI tools can automate portions of that work. Some can operate continuously and pursue multiple potential targets at once. As a result, companies may have less time to respond when criminals discover a way into their systems.

Microsoft exposes AI cyberattacks moving at machine speed

One of the clearest examples comes from Microsoft. On Oct. 21, Microsoft Threat Intelligence revealed that a China-state-aligned hacking group called Storm-0940 had used an AI-powered penetration testing framework called ARTEX. The open-source tool can automate security testing tasks, including investigating networks and identifying potential weaknesses. In the hands of criminals, those capabilities can accelerate attempts to gain unauthorized access.

According to Microsoft, the group used ARTEX to target hundreds of organizations across multiple industries. Several attacks resulted in unauthorized privileged access to cloud systems. In multiple cases, attackers reached that level of access in less than three hours. Although many attempts failed, the successful intrusions demonstrate how quickly AI-assisted attacks can unfold.

Hackers launch thousands of login attempts per minute

Between Oct. 10 and 14, Microsoft recorded more than 151,000 failed login attempts in one campaign targeting 327 accounts across eight organizations. At its peak on Oct. 11, attackers generated approximately 2,900 failed login attempts per minute. The technique, known as password spraying, involves trying passwords against multiple accounts to identify a working login.

Importantly, Microsoft did not observe successful logins during that specific campaign. However, it documented unauthorized access and suspicious activity in other environments associated with the same threat group. Microsoft also connected Storm-0940 to a compromise involving ConnectWise, a company that provides software used by IT service providers. Attackers exploited access associated with ConnectWise cloud applications to attempt entry into customer environments. Some then carried out further activity through Microsoft cloud services, including changes that could help them maintain access.

Microsoft cautioned that suspicious access does not automatically mean customer information was stolen. Nevertheless, the activity reveals how AI can help attackers move quickly once they obtain usable credentials.

A $449 AI account scare shows the financial danger

The risks become more personal when you look at what happened to Colin Parsons. Parsons reportedly woke up to roughly 50 notifications about charges involving OpenAI and Anthropic. He reported $281 in unexpected OpenAI usage and another $168 involving Anthropic. Both credentials were associated with OpenCode, an AI coding platform he used.

On Oct. 17, OpenCode disclosed a security incident involving its Console service. The company said unauthorized access to a legacy system may have exposed third-party AI provider keys stored by some users. The company reportedly notified affected customers and advised them to revoke their credentials.

OpenCode said the incident affected approximately 1.4% of its Console users who had connected external AI providers. The disclosure concerned credentials stored in Console, rather than keys stored locally in OpenCode's desktop or command-line applications. Other users also reported unexpected charges, although the amounts have not been independently verified. OpenCode associated its incident with a large-scale AI model distillation attack, but it has not publicly established exactly how the reported unauthorized usage occurred.

The concern is straightforward. If someone obtains a working API key, they may be able to use a paid AI service and generate charges against the account owner's billing arrangement. For people who depend on AI tools for work, that can become expensive before they realize anything has happened.

WINDOWS MALWARE USES GROK AI TO HELP STAY HIDDEN, RESEARCHERS SAY

A massive website security scare adds to Black October fears

While hackers are becoming more capable, AI-assisted security research is also uncovering dangerous weaknesses in software that supports the internet. On Oct. 21, developers released emergency fixes for two critical vulnerabilities in PHP, a programming language widely used to operate websites.

The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, are collectively known as PHP2Shell. Under certain conditions, the flaws could allow attackers to execute malicious code on vulnerable servers without first signing in. Successful exploitation could expose sensitive information or give criminals control over affected systems.

The potential impact is enormous because PHP powers roughly 70% of websites whose server-side programming language is known. However, that does not mean 70% of websites were hacked. It also doesn't establish that attackers could successfully compromise every website using PHP. The vulnerabilities affect PHP installations handling web requests, but successfully exploiting them can require complex technical conditions.

Federal agencies issue urgent security warnings

The situation prompted warnings from U.S. cybersecurity authorities. On Oct. 23, the FBI issued a public alert urging organizations to patch affected systems immediately. The Cybersecurity and Infrastructure Security Agency also called for urgent updates. The PHP project released fixes in versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Website administrators running older unsupported versions need to obtain appropriate vendor-supported fixes or migrate to a supported release.

Meanwhile, several government organizations in Europe temporarily took websites offline as a precaution. However, the situation became clearer as researchers investigated. On Oct. 23, the Netherlands' National Cyber Security Centre said exploiting the vulnerabilities appeared more complicated than initially feared. The agency lowered its assessment of the likelihood of widespread exploitation.

Also on Oct. 23, PHP disclosed a separate vulnerability, CVE-2026-115560, involving an unusual combination of server settings and application code. The project recommended a temporary configuration change while it prepares a fix through its regular release process. Website owners should continue following official PHP security guidance rather than assuming the emergency has completely passed.

Cybersecurity firm CrowdStrike also reported seeing attempted attacks, but said it had not observed successful exploitation of PHP2Shell in its investigations at that point. Other security researchers, including Amazon Threat Intelligence, observed suspicious exploitation attempts beginning before the patches became publicly available. Those attempts remain important even without proof that they successfully compromised real systems.

However, new evidence emerged over the following days. On Oct. 24, security researcher Adel Karimi documented successful PHP2Shell exploitation against specially configured test servers, known as honeypots. The attacks launched 35 command shells across three honeypots. Although those findings did not establish how many real-world websites had been compromised, they demonstrated that attackers could successfully exploit the vulnerability under certain conditions.

Then, on Oct. 26, CISA added both PHP2Shell vulnerabilities, CVE-2026-109618 and CVE-2026-109619, to its Known Exploited Vulnerabilities catalog. The designation confirms that federal authorities recognize evidence of active exploitation. It also reinforces the urgency of installing security updates, even though the full extent of attacks against real-world systems remains unclear.

AI is helping hackers, but security researchers are using it too

There's another side to this story that deserves attention. Artificial intelligence helped researchers investigate the PHP vulnerabilities before the October emergency. According to the PHP Foundation, developers had identified early signs of one underlying problem during a security investigation in 2024. However, the team struggled to develop a reliable solution. Additional research in 2026 exposed the seriousness of the issue.

The foundation worked with researchers and used AI-assisted security tools, including technology from Anthropic and OpenAI, to examine PHP's code. Researchers from security companies Calif and Wiz also contributed important findings. The PHP Foundation says these reports helped clarify the vulnerabilities' potential impact and accelerated the work needed to release fixes.

AI can therefore help defenders identify dangerous weaknesses before criminals exploit them. The challenge is ensuring security teams can investigate the findings and distribute fixes quickly enough. That challenge is becoming more urgent.

What AI-powered cyberattacks mean for your personal information

You may be wondering how any of this affects you if you're simply checking email or shopping online. The concern starts with the companies holding your information. When hackers compromise a business, they may gain access to stored customer information. Depending on the systems involved, that could include email addresses or passwords. Financial details may also be exposed. Criminals can use stolen information to launch convincing scams or attempt to take over existing accounts.

Meanwhile, AI makes it easier to produce personalized phishing messages. Attackers can incorporate leaked information into emails that appear to come from a company you recognize. Some criminals also use AI-generated voices to impersonate people and pressure their targets into making payments.

However, a security vulnerability affecting a website doesn't automatically mean your personal information has been exposed. The actual risk depends on whether attackers successfully gained access and what information they obtained. That's why it helps to focus on the steps you can control.

HACKERS HIDE DANGEROUS FAKE AI DOWNLOADS BEHIND GOOGLE ADS

8 ways to protect yourself from AI-powered cyberattacks

You can't personally fix security problems affecting large companies. However, you can strengthen your accounts and reduce the potential damage if criminals obtain your information. Here are seven precautions I recommend taking now.

1. Secure your most important accounts first

Start with your primary email account. Criminals who gain access to it may be able to reset passwords for other services you use. Create a strong, unique password for every account. A reputable password manager can help you generate and store those passwords. Next, enable multifactor authentication wherever it's available. Passkeys and hardware security keys offer especially strong protection against phishing. Authenticator apps are another useful option. Avoid relying on passwords alone.

2. Check whether your passwords have been compromised

Your phone may already have tools that can identify passwords exposed in known data breaches. On an iPhone, open the Passwords app and review its Security section. Android users who save passwords through Google can review warnings in Google Password Manager. If a password has been exposed, change it directly through the company's official website or app. Also update any other accounts using that same password. Our article explains how to find compromised passwords on iPhone and Android. Remember, a compromised-password warning does not necessarily mean someone has accessed your account. However, it gives you a chance to replace a vulnerable login.

3. Watch your accounts for suspicious activity

Enable transaction notifications through your bank and credit card providers. Also review recent sign-ins on your email accounts and other important services. Watch for unfamiliar devices or changes to your recovery information. If you spot unauthorized activity, contact the provider through its official website or app. Change affected credentials and revoke unfamiliar sessions where possible. Don't wait for several suspicious charges before investigating.

4. Review which apps can access your information

Many people connect third-party apps to their Google or Microsoft accounts without thinking about the permissions they're granting. Over time, those connections can accumulate. Some applications may retain access even after you've stopped using them. Open your account's security settings and review connected applications. Remove access you no longer need or recognize. However, if a service you use has announced a security incident, follow its specific recovery instructions. Simply disconnecting an app may not revoke credentials that attackers already obtained.

5. Use strong security protection and monitor your identity

Strong antivirus software can help detect malicious downloads and block dangerous websites. However, antivirus protection cannot prevent every account takeover or stop a company from experiencing a data breach. That's why monitoring your financial information is also important. Consider placing a free credit freeze with Equifax, Experian and TransUnion to help prevent criminals from opening new credit accounts in your name. Keep in mind that a freeze won't protect accounts you already have. If you use AI services that require API keys, review your usage regularly. Revoke credentials that may have been exposed and set billing alerts or limits where the provider supports them. Get my picks for the best 2026 antivirus protection winners for your Windows, Mac, Android and iOS devices at CyberGuy.com.

6. Consider using a personal data removal service

Data brokers collect and sell personal information, including phone numbers and home addresses. Criminals can use those details to make AI-generated scams more convincing. A personal data removal service can help remove your information from people-search sites and data broker databases, making it harder for scammers to find. However, it can't erase information from past breaches or prevent cyberattacks. Check out my top picks for data removal services and get a free scan to find out if your personal information is already out on the web by visiting CyberGuy.com.

7. Keep your devices and software updated

Enable automatic security updates on your phone and computer. Keep your browser current, too. Updates frequently fix vulnerabilities that criminals may try to exploit.

8. Be skeptical of urgent security messages

AI-generated phishing messages can look remarkably convincing. They may contain personal information that makes them appear legitimate. Be cautious if someone unexpectedly claims your account has been compromised or demands immediate payment. Instead of clicking a link, open the company's official app or visit its website directly. Never share a verification code with someone who contacts you unexpectedly. Criminals often create pressure because they want you to act before checking the details.

Kurt's key takeaways

What concerns me most about this wave of AI-powered cyberattacks is the speed. Microsoft documented attackers gaining privileged access in less than three hours. That's a frighteningly short window for companies to react. At the same time, AI is helping security researchers uncover weaknesses before criminals exploit them. But here's what worries me. We trust companies with enormous amounts of personal information, yet we're often left dealing with the fallout when their security fails. I believe those companies need to be held more accountable. Until then, protecting our accounts and staying alert to suspicious activity remains our best defense.

If AI allows hackers to attack thousands of accounts in minutes, should companies face tougher penalties when they fail to protect our personal information? Let us know by writing to us at CyberGuy.com.

Sign up for my FREE CyberGuy Newsletter

  • Get my best tech tips, urgent security alerts and exclusive deals delivered straight to your inbox.
  • For simple, real-world ways to spot scams early and stay protected, visit CyberGuy.com – trusted by millions who watch CyberGuy on TV daily.
  • Plus, you'll get instant access to my Ultimate Scam Survival Guide free when you join.

CLICK HERE TO DOWNLOAD THE FOX NEWS APP

Copyright 2026 CyberGuy.com. All rights reserved.
  •  

Tennis star Genie Bouchard kicks off Halloween weekend with Britney tribute, Caleb supports kids & beer sword

Welcome to Screencaps, "America's Best Daily Column," as named by the readers. Screencaps, which publishes seven-days-a-week, is a mix of sports, pop culture, and emails from sane readers from around the world. This column isn't for the coastal elites. Give us a week to steal your heart. Our track record is pretty good. Let's have some fun.

Welcome to one of the greatest times of the year for Screencaps

It's like shooting fish in a barrel right now for this column. I was telling Mrs. Screencaps this week that there are days of the year I don't like to take off work because the content is just so good. Those days include the holidays and Halloween.

Why wouldn't I take off the holidays? 1. It's my column. I don't feel like it's fair to SeanJo to tell him to work the holidays when I started this column. 2. The content is always great. July 4? Are you kidding me? The content is off the charts. Christmas? Instagram models dump out all sorts of content. New Years? Having to work in the morning tends to prevent me from going too nuts the night before. Thanksgiving morning is one of the easiest editions of Screencaps to produce. People are in a good mood. They want to show me what they're cooking.

CARMEN ELECTRA OFFICIALLY KICKS OFF HALLOWEEN SEASON AT A GAS STATION, POSTGAME POLICE CHASE & BALL-SAC

And they're dialed into the content because they're not at work.

As for Halloween, I literally get paid to report on Halloween costumes. After being told this week by some idiot emailer that I should retire, my resolve is stronger than ever. No, I won't retire. I built this column into the greatest job on the Internet. You'd have to yank it out of my cold dead hands.

Thank you to retired tennis star Genie Bouchard for kicking off the weekend with a Brit Brit tribute. Well done.

📩 Email: joe.kinsey@outkick.com
Send photos, stories, tips, rants—whatever you've got.

📰 Screencaps Page:
👉 Read the latest Screencaps

Mailbag: How do you deal with the a--holes?

– Jayson asks: A buddy of mine writes a mailbag column for a website. He said that occasionally, he will get emails from "psychos" who flip on him for not reading their questions. Have you ever received that kind of junk since starting Screencaps? If you do, do you answer them back, or simply ignore them?

Kinsey: I've never had emailers turn heel because I wouldn't publish their emails, but I've had guys who claimed to be fans and loyal readers who turned out to be total scumbags, especially after I left Busted Coverage and joined Clay Travis here at OutKick. There have been guys who felt like I should've given them freebies that brands used to send to me.

As for a--hole emailers, I like when people write and snap on me. It's great content. Typically, when I reply to their emails, the people disappear.

WARREN SAPP GETS INTO CONFRONTATION WITH FLORIDA STATE FAN DURING TAILGATE, TIM MCGRAW'S BRONZER & DALE ART

This is a career-low and she's playing COLLEGE golf

A quick Google search reveals that Elizabethtown College was having revenue trouble in 2024 when the school cut 13 faculty members. You know what they didn't cut? Women's golf, where members of the team are really killing it out on the links.

Do you let weirdos pick your groceries and dump them into your car?

• Legacy reader Jess in Alabama, who has been emailing longer than pretty much any other OutKick reader, says it's just convenient: The guy who wrote in that only the elderly or disabled should get delivery groceries is forgetting the time in his life with babies. I can get off my lazy ass, but y’all don’t want to see that diaper blowout spill on the aisle next to your shoe or hear the tantrum that happens 1 out of 4 trips. I’ll let the grocery guy pick out a bag of potatoes or mustard or random stuff I grab off the shelf. Then I’ll find time to stock my own meat and fruit when I get a chance. And I am not complaining about my life. I’m very grateful. And very grateful not to ruin your pleasant experience at the grocery store.

SUPERMARKET VOTED BEST GROCERY STORE IN AMERICA AS CUSTOMERS PRAISE MEAL KITS, VARIETY OF OFFERINGS

• Louie in Savannah pushes back on Chris A.'s email: I have been following along with the grocery pick up debate the last few days and have to weigh in, especially after the comment about those that do it are lazy and park in the fire lane.

We use it every week. We are quite able-bodied, just busy as hell.

BABY BOOMERS HATE 10 THINGS ABOUT TODAY'S GROCERY STORES

My wife is the "Food and Beverage Coordinator" in our home and we have been using the Kroger "Click list" just about every week since it became an option years ago. I imagine every store in different parts of the country have varying experiences but there are so many benefits for us to ordering online and picking it up. My wife just submitted ours and I'm picking it up on the way home from work tomorrow. I'll be in the parking lot for no more that 15 minutes total. It's very convenient and actually saves money. There is no impulse buying when you pick it up, only what you ordered. We also aren't bringing our teen and pre-teen sons into the store who are suddenly starving (as always) and now want to throw everything they see into the cart and grab a sushi roll to devour while walking around. As an added bonus, once every two months or so, the store accidentally loads someone else's partial order into the car and there is no way to tell until you get home. It is like a bonus mystery box. We always call to let them know but they always say to keep the items.

Sure, there are issues with produce or other things sometimes but the customer service personnel are always nice and they will throw a $20 coupon into the next order for the inconvenience. Also, beer and wine purchases are allowed as well so that is one fewer stop while running errands.

With as busy as we are in my house with jobs, school and sports, grocery pick up saves a ton of time!

Everywhere is different I am sure but it's a huge benefit for our house.

• Voiceover Mike writes: To be honest, my wife will put in a weekly Target order, something of a holdover from Covid days, and I'm usually the one on pick-up duty. Do I feel a little emasculated, sitting next to soccer moms in their SUVs and Teslas waiting for their orders? Maybe a little. Will I let the Target order picker select produce for me? Nope. I hit the grocery store for that.

If it were my choice, I'd wander the aisles, list in hand, and pick everything myself, but I've been relegated to pick-up duty. Keep up the great work, and never underestimate the importance of what you do for us.

• Tom T. is fired up: Nice fall weather hare in VA. It’s a good day to shake my old man fist at the clouds.

Chris A. really nailed it! Get off your lazy butt and go get your own damn groceries! Also, if you are under 40 and would like to one day own a home, get off your lazy butt and go get your own damn groceries, and then COOK your own damn food. I just do not get the allure of Door Dash, unless you have been drinking beer all day, because nobody should be drinking and driving in this day and age. Also, make your own damn coffee in the morning.

I also LOVE the entitled losers who park in the fire lane while their spouse "runs" into the grocery store "for one thing". I always give ‘em the hairy eyeball as I walk into the grocery store.

• Bob in Cincy says: Our strategy for groceries is to leverage the Kroger pickup for staples such as canned good, frozen items and the like.  No veggies or fruits.  For those we go to Dorthy Lane or Fresh Thyme which are more expensive in general.  The online shopping is convenient I’ll admit, and less expensive than DL or FT.  It works well for us.

Resealable cereal bags were finally invented

• Joe in E. Tennessee checks in: What am I going to do with the twenty or so chip clips that are currently keeping my cereal fresh!?!? I'll run out of room on my refrigerator!!!

Kinsey: The Big Chip Clip lobbyists will not stand for these resealable bags. Just wait. Congress will intervene.

ZERO BS. JUST DAKICH. TAKE THE DON'T @ ME PODCAST ON THE ROAD. DOWNLOAD NOW!

Fall golf

• Darren in NE ATL shares: Had almost forgotten a fall golf memory. Late fall in the 90's, with my dad, north of Dover, DE. Probably low 40's. Pushed a drive near a lake into clumped grass. Got there and a slow moving, big ass snake was right at my ball. Seeing as my one true phobia is snakes, I took a stroke penalty for a lost ball, and ran the he'll away.

################

SIGN UP FOR THE DAILY OUTKICK NEWSLETTER

That is it this morning. What a morning it has been. Mrs. Screencaps, whose birthday is Sunday, has been sick on and off all week and she's dealing with a sore back. It takes a village around here, that's for sure. But, we made it through another week of life.

OUTKICK IS NOW AVAILABLE ON THE FOX NEWS APP: CLICK HERE TO DOWNLOAD

Let's go have a great Halloween, if you celebrate. I have one more morning to go. Tomorrow morning will be 13 straight editions of Screencaps before I get to turn off the alarm Sunday morning. Let's finish strong.

Numbers from :

Stuff You Guys Sent In & Stuff I Like :

  •  

Brewers continue World Series celebration, raise Commissioner’s Trophy at Lambeau Field during Packers game

Less than 24 hours after the Milwaukee Brewers captured the franchise’s first World Series title, the team’s celebration continued roughly 120 miles north at Lambeau Field.

Brewers pitcher Brandon Woodruff brought the Commissioner’s Trophy onto the field Thursday night at the end of the first quarter of the Green Bay Packers’ game against the Carolina Panthers. Teammates Christian Yelich and Sal Frelick also joined the celebration.

Frelick embraced the moment by attempting a Lambeau Leap of his own, drawing a warm reaction from the Packers faithful.

BREWERS STAR CHRISTIAN YELICH PAYS TOUCHING TRIBUTE TO LATE, BELOVED BROADCASTER AFTER WORLD SERIES WIN

Milwaukee could come to a standstill Friday, with thousands of fans expected to line the streets for a victory parade celebrating the Brewers’ long-awaited championship.

Wisconsin’s largest school district, Milwaukee Public Schools, announced it would close Friday, citing operational and safety concerns. However, the closure will also give faculty and students the opportunity to enjoy the parade.

THE CRAIG CARTON SHOW–UNFILTERED, UNAPOLOGETIC AND UNMISSABLE. DOWNLOAD HIS DAILY PODCAST NOW!

CLICK HERE FOR MORE OUTKICK SPORTS COVERAGE

The parade route will run through downtown Milwaukee before ending with a fan fest at Henry Maier Festival Park.

The Packers are likely hoping to build on the Brewers’ success, despite not having won or reached a Super Bowl since the 2010 season.

The Brewers’ Game 5 victory over the Tampa Bay Rays to clinch the World Series title and the Bucks' 2021 NBA Finals victory means the Packers now own the longest championship drought among Wisconsin’s major men’s professional sports teams.

SIGN UP FOR THE DAILY OUTKICK NEWSLETTER

Green Bay entered Thursday night’s game coming off a Week 7 loss to the Detroit Lions. The Panthers jumped out to a 3-0 first-quarter lead. The Packers responded by taking a 20-10 halftime lead and extending the advantage to 27-10 in the third quarter.

  •  

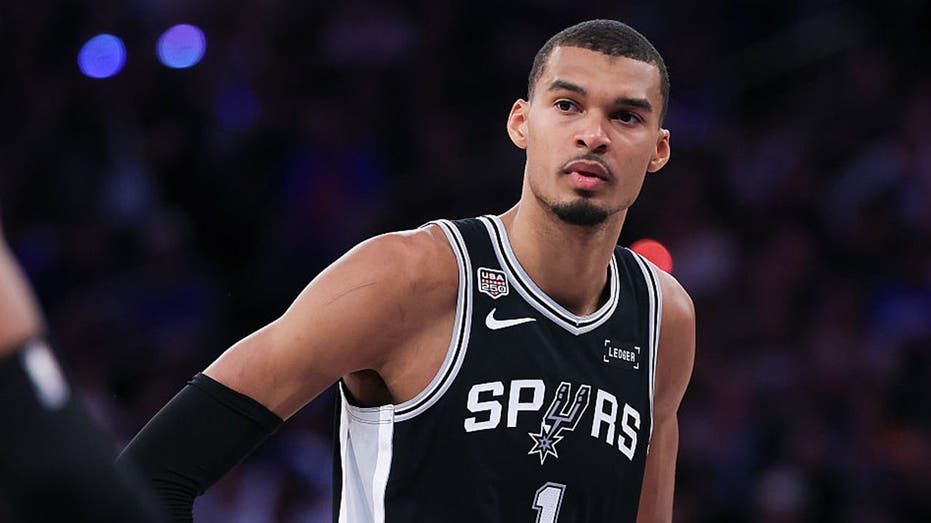
Spurs' Victor Wembanyama embraces competitive edge but rejects villain label after NBA playoff lessons

Victor Wembanyama is unquestionably one of basketball's brightest young stars. In his third NBA season, he led the San Antonio Spurs to the Finals.

San Antonio ultimately lost the series to the New York Knicks in five games. Wembanyama earned several individual honors, including his first Defensive Player of the Year award and All-NBA selection.

The French-born Spurs forward opened the 2026-27 season under enormous expectations. The 7-foot-4 star was a preseason favorite to win the NBA MVP award, while San Antonio entered the season as an odds-on favorite to win the championship.

The postseason also marked a notable shift in how the public viewed Wembanyama. Once a widely beloved sports figure, he was increasingly cast by some as a villain.

SIGN UP FOR THE DAILY OUTKICK NEWSLETTER

A series of on-court incidents fueled claims that Wembanyama had become a "dirty" player. One of those situations surfaced in the Western Conference semifinals, when his elbow made contact with then-Minnesota Timberwolves center Naz Reid.

During the Finals, many Knicks fans grew furious at times over Wembanyama’s defense against Jalen Brunson.

Once viewed as a conquering hero, Wembanyama was quickly cast as a New York sports villain. But he insisted the criticism does not faze him.

"No, it didn't because I'm not paying attention to this ... during the Finals. I don't think any player on either team really is," Wembanyama told "60 Minutes" when asked about his portrayal as a villain in a clip released Thursday ahead of Sunday’s full sit-down interview.

THE CRAIG CARTON SHOW–UNFILTERED, UNAPOLOGETIC AND UNMISSABLE. DOWNLOAD HIS DAILY PODCAST NOW!

Although Wembanyama said he tunes out much of the noise, he does not appear eager to let the villain label stick. He added that last season’s playoff run taught him where to draw the line between playing with a competitive edge and going a step farther than he should, acknowledging that he crossed it at times.

VICTOR WEMBANYAMA ADMITS TO HARSH TRUTHS AFTER COSTLY MISTAKE AT END OF NBA FINALS GAME

"It showed my limits more than anything else. Going out there, you need to play basketball. You don't need to beat the s--- out of people. [laughs] If you wanna win, at least," Wembanyama said while reflecting on the lessons he learned from last season’s playoff run.

Wembanyama also drew public attention before some Finals games began. He was seen standing with his arms crossed during the U.S. national anthem before Game 1, but reportedly was not on the court for the anthems before Games 3 and 4.

He has not publicly explained why he stood with his arms crossed before Game 1 on June 3. Wembanyama has played in all five of San Antonio’s regular-season games this season, averaging 25 points per game.

CLICK HERE TO DOWNLOAD THE FOX NEWS APP

The Spurs return to action Saturday, when they host the Timberwolves.

  •  

Rampaging longhorn causes pileup on local road in Putnam County, leads police on wild chase

I think I speak for everyone when I say that traffic jams are the absolute worst.

There is nothing more infuriating than coming home from work or driving to an event like a game or a concert and seeing nothing but brake lights ahead.

If you're anything like me, after the blinding rage wears off, you often wonder what caused the jam to begin with.

Usually, it's because some idiot missed his exit and decided to merge across six lanes of traffic or a college kid who's home on break was texting and driving before rear-endeding someone, but how about when a longhorn busts loose from the farm and leads the cops on a wild chase across a two-lane road?

What, you've never had that happen to you before?

MISSING 1200-POUND GIRAFFE GRACIE FOUND 2 WEEKS AFTER WANDERING AWAY FROM RANCH IN VIRAL SEARCH

It turns out several of the motorists in Putnam County, New York, were treated to a traffic jam of bovine origins when a four-year-old cow named Maggie caused a pileup when she escaped from the friendly confines of Little Cabin's Farm in nearby Carmel, NY.

The video is absolutely hysterical (mostly because I'm not the one behind the wheel) and features police cars and civilians alike trying (and failing) to wrangle the clearly agitated animal as she darts in between several stopped vehicles.

One of the civilians is even seen brandishing a tree branch to use as a whip to try and corral Maggie back onto the other side of the road.

While traffic is at a dead stop in the one lane, the oncoming lane has cars driving at full speed, and one of them even had to slam on their brakes as Maggie scampered back to the grassy shoulder.

THE CRAIG CARTON SHOW–UNFILTERED, UNAPOLOGETIC AND UNMISSABLE. DOWNLOAD HIS DAILY PODCAST NOW!

VIRAL VIDEO SHOWS MASSIVE BISON POPPING TOURIST VEHICLE'S TIRE IN YELLOWSTONE NATIONAL PARK

She's lucky some Kia didn't turn her into ground beef!

According to local news affiliate WABC, Maggie was on the loose for four days before finally being brought home, giving drivers all over Putnam County a reason to breathe easier.

SIGN UP FOR THE DAILY OUTKICK NEWSLETTER

What's even crazier is that Maggie is also pregnant, which might explain some of her erratic behavior.

CLICK HERE TO DOWNLOAD THE FOX NEWS APP

All's well that ends well, though, and it's nice to know she's back on the farm where she belongs.

  •  

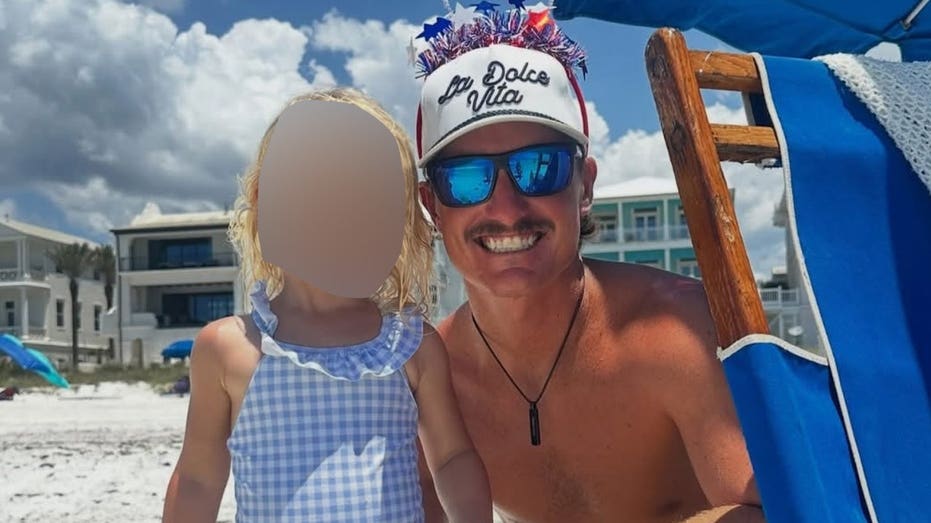
Florida dad who swam to tangled seagull and was carried away from shore drowns

A father who swam out into the sea to help untangle a seagull from his fishing line drowned and died after an ocean current swept him away, Fox 5 Atlanta reported.

Atlanta area native Stone Romberg was fishing at his home in the Florida Panhandle when he noticed the seagull caught in his fishing line, Fox 5 reported.

The 31-year-old father of two swam out to try and untangle the bird, but his hook and the bird got stuck to his hand while he tried to help. As he tried to swim to shore, an ocean current carried him further out to sea where he tragically drowned.

"Our hearts are broken for everyone who knew and loved him," a GoFundMe set up for his family reads.

MOM OF 2 WHO DIED RESCUING SONS DURING BAHAMAS SNORKELING TRIP IS IDENTIFIED

Romberg was the manager of chair services at a local condominium complex and "was known by a lot of our owners and guests," according to the GoFundMe.

A Facebook page for his workplace also shared that he will be remembered "for his kind heart, hard work, and willingness to always lend a hand."

THREE MEN GET 158 YEARS EACH FOR MURDERING AMERICAN AND AUSTRALIAN SURFERS, DUMPING BODIES IN MEXICAN WELL

"His kindness left a lasting impression on everyone who knew him, and he will be deeply missed," the post also read.

The GoFundMe set up for his family, who relied on him for financial support, has raised $138,714 as of Thursday afternoon.

He is survived by his wife Taylor and his one-year-old and three-year-old girls.

CLICK HERE TO DOWNLOAD THE FOX NEWS APP

Romberg was an avid fan of SEC football and the Atlanta Braves, according to Fox 5.

  •  

Reddit users reveal 'rich people' habits they tried once and could never go back from

What's a spending habit rich people have that is totally worth it?

As the loyal readers know, I am a big fan of Reddit. When it comes to places on the internet where you can find yourself going down deep rabbit holes, there's probably no place that beats Reddit.

You simply never know what you're going to find. There are plenty of crazy stories, history lessons and really cool military content on Reddit.

REDDIT THREAD ON LIFE CHEAT CODES GOES VIRAL WITH ADVICE ON FITNESS, SLEEP AND COMPOUND INTEREST

There's also plenty of debates and discussions, and that's what leads us here today.

Convenience habits of rich people go viral on Reddit

I was scrolling the r/askreddit subreddit early Thursday morning when I stumbled across and interesting thread title that caught my attention:

AMERICANS SAY THEY'RE BROKE. SO WHY CAN'T THEY STOP SPENDING SO MUCH?

What's a 'rich people' thing you tried once and immediately understood why they do it?

As someone interested in money (aren't we all, after all?), it was an instant click from me. The results didn't disappoint at all.

Let's check out some of the replies before breaking it down:

  • I drive a Lexus. Oh, wait, it's 20 years old. Regardless I feel like a princess behind the wheel.
  • Ordering groceries that arrive pre chopped, pre washed, and neatly portioned. I laughed at the price tag once, tried it during a burnout week, and instantly understood. It’s not buying food it’s buying back two hours of your Sunday so you don't spend it crying over a cutting board.
  • Don't ever fly business class on a long haul flight unless you can afford to do it regularly. Once you know... economy sucks so much harder.
  • Custom made clothes. Had a dress made for a special event. Fit me like a glove, looked perfect on me, and I felt like a queen. Would get my whole wardrobe custom made if I had them money.
  • Flew private. Our organization has a small place and the pilots have to have a certain number of flight hours per month so we asked to fly to a regional meeting. I parked, walked in, waited for the plane to land, got a short safety briefing, then walked 30 feet to the plane and boarded. No one even checked my ID. I 100% understand why people do this. It was so so nice not to have to deal with airport parking, TSA, or loading a commercial plane (where I always fly cheap af).
  • Hiring movers. Not sure if this counts, but I hired a moving company to move my stuff for the first time. Was like half a garage and a rooms worth of stuff. $500 later and it’s just where you need it to be. Parents divorced when I was young. They seemed to lease a new house every year, so lots of moving. Finally realized it doesn’t have to be a terrible process and I can just have someone else do it all and it’s so worth it.
  • Flying first class. Apparently the difference between hating air travel and enjoying it is about six inches of legroom and a glass of champagne.
  • What I'm getting from this thread is that flying is miserable if you're not rich
  • I bought a bespoke suit. Made me look like James Bond. And ruined off the rack suits for me. You essentially don't want to wear anything else.
  • Anything above economy for long haul flights. I just did premium economy and the difference was enough to nearly spoil me. I can't imagine how it feels in business and first.
  • I bought vip packages to a music festival. Was like $10 a person extra with access to private lounge and things. I only did it for the great access bathrooms. That alone was easily worth it to me.
  • Cleaning lady. Never did it myself, but I dated a woman with a cleaning lady. Picked her up at a messy home, had a nice time out, came back to a spotless home. Unbelievable experience. If I ever have money, cleaning lady.
  • Went to the warmer states during the winter months.
  • Taking a $40 uber right to my destination instead of having to take a bus to a train to a bus and walking several blocks.
  • Eating at a really nice restaurant. I am talking about a Michelin star restaurant. I went to one on a work trip once.
  • Hiring a moving company
  • Having someone clean your house for you. I finally understand why rich people pay for convenience.

Now, as the readers also know, I'm a working class guy from rural Wisconsin. You grow up fast when you grow up in those harsh winters. Life doesn't have many luxuries and you learn to get by with what you have.

Having said that, I have tasted the high-life once or twice, and without question flying first class is the obvious answer to this viral Reddit question.

Are there much more expensive things rich people have access to? Sure, but flying first class is attainable for most people if they want it to be, and it makes the flying experience significantly better.

Not a little bit better.

Much better.

Taking a seat on a first class flight – I've always found Delta to be the best – and being immediately greeted with a snack and drink instantly makes the hellish airport experience better.

SIGN UP FOR THE DAILY OUTKICK NEWSLETTER

It's almost impossible to go back once you've been in first class.

OUTKICK IS NOW AVAILABLE ON THE FOX NEWS APP: CLICK HERE TO DOWNLOAD

What's your splurge item that wealthy people enjoy? Let me know at David.Hookstead@outkick.com.

  •  
❌