The largest cyber heist in history came as attackers increasingly use artificial intelligence and other advanced techniques to steal crypto and quickly launder the funds.
The founder of Binance, Changpeng Zhao, in Hong Kong in August. The company, the world’s biggest crypto exchange, has promised to make customers whole.
Hackers made off with around $6 billion in digital currency in what could be the biggest crypto heist in history. Binance said it will cover the losses.
Binance, the world's largest cryptocurrency exchange, suspended withdrawals after hackers stole $6 billion from its digital wallets in what is being described as the biggest financial heist on record.
A hacker going by the name "Department of Peace" has published personal data belonging to more than 40,000 U.S. Department of Homeland Security employees, exposing ICE agents, cybersecurity staff and senior officials to potential harassment and violence.
A CPES avaliou o risco em julho, antes das novas ameaças ao hacker do Football Leaks. A defesa só pôde pronunciar-se a 23 de outubro, mas a primeira decisão deverá manter-se.
You send your child to school expecting teachers to protect their education. You probably don't think much about what happens to their personal information after they take a standardized test. But a massive data breach in California is raising some uncomfortable questions about who has access to student records and how safely that information is stored.
Hackers accessed and copied sensitive records belonging to millions of current and former California public school students. The stolen information includes home addresses, birth dates and even details about disabilities. And here's something families need to know. You could live thousands of miles from California today and still be caught up in this breach if you or your child previously attended a public school there.
Join our upcoming CyberGuy LIVE class: 5 Ways to Travel Smarter and Save Money
In this free live online class, Kurt "CyberGuy" Knutsson will share five practical ways to protect your trip and your wallet this holiday travel season. You’ll learn how to secure your phone and personal information, find better travel deals, avoid common scams, save money on bookings and use technology to make your travels easier and less stressful. No technical experience is needed.
Join us Saturday, October 31, at 11 AM ET / 8 AM PT. Register for free now at CyberGuyLive.com.
How millions of California student records were stolen
The breach involves Educational Testing Service (ETS), a nonprofit organization that works with the California Department of Education. ETS helps administer statewide student assessments and maintains information connected to those tests. According to state officials, someone gained unauthorized access to an ETS-operated secure file transfer site. Investigators determined that the attacker used a compromised login credential to enter the system. The intruder then copied files containing student information at various times between May 22 and Sept. 18, 2026.
ETS discovered the suspicious activity on Sept. 25. The company disabled the affected account and took the file transfer site offline. It also brought in outside cybersecurity specialists to investigate. The company says it has since built a replacement system with stronger security controls. So far, ETS reports finding no evidence that the stolen information has been made publicly available. However, investigators have confirmed that someone accessed and copied the records.
What personal information was stolen in the student data breach?
The California student data breach involved far more than test scores. Depending on the student, the compromised files may contain information that could help someone identify a child or learn personal details about their family circumstances.
The exposed records may include:
Student names and dates of birth
Home addresses, school names and grade levels
Statewide and local student identification numbers
Race, ethnicity and primary language
Country of origin and English learner status
Disability information and testing accommodations
Participation in certain educational assistance programs
Statewide assessment participation and test results
Some records also identified whether a student qualified for programs serving children experiencing homelessness or other educational needs. Fortunately, officials say the stolen files did not contain Social Security numbers, financial account details, driver's license numbers, passwords or parent and guardian personal information.
However, there is still plenty to be concerned about. Someone who knows a child's name, school and address could potentially use that information to create a convincing message that appears to come from a teacher or school administrator. Disability information also raises additional privacy concerns because those details are particularly personal.
Why this California breach could affect families nationwide
This is where the story gets especially troubling. Although the breach involves California's public school system, the people whose records were stolen may now live anywhere in the United States. According to the California Department of Education, the compromised information includes records covering all students enrolled during the previous three school years. However, the affected population extends beyond those students.
The state also identifies a group of former students who left California public schools as far back as 2006 and whose transfers to another school were never confirmed with the department. That creates a situation many families may never have considered. Say your child attended elementary school in Los Angeles before your family relocated to Texas. Perhaps you graduated from a California public school years ago and now live in Florida. Your old student information could still be among the compromised records if it falls within the affected groups.
Former students who are now adults may also be eligible for the free identity-protection services being offered. Importantly, this does not mean every student attending school outside California has been affected. In a statement to CyberGuy, ETS confirmed that no other ETS customers were affected by the incident. The concern for families elsewhere comes from their past connection to California's public schools. California has roughly 5.7 million public school students, according to reporting on the breach. Since the compromised files span multiple school years, millions of people are potentially involved. Officials have not yet released a final count of unique affected individuals.
Where the student data breach investigation stands
The California Department of Education and the State Board of Education are coordinating with cybersecurity specialists and other state agencies. The California Cybersecurity Integration Center is assisting with the technical investigation. Meanwhile, state officials are reviewing ETS's compliance with applicable data security requirements and its contractual obligations.
In its statement to CyberGuy, ETS said, "We have implemented additional safeguards, including enhanced monitoring, strengthened access controls, and further third-party review of our security practices." ETS says it continues monitoring for signs that the stolen information has surfaced publicly. For families, the unresolved question is what happens to the copied information next. Even without evidence of a public leak, sensitive student records in unauthorized hands create a privacy risk that deserves continued attention.
ETS began notifying affected students and families on October 16, 2026. The state expects notifications to continue through early November. Letters and emails will explain the incident and identify the types of information involved. They will also include instructions for accessing complimentary identity-protection services. However, here's an important warning. Not receiving a notification does not necessarily mean your information is safe. Some former students may have outdated contact information on file.
Families who are concerned should visit the official California ETS incident webpage. It contains frequently asked questions and links to breach notifications available in 27 languages. You can also call the incident assistance line at 833-931-8488, Monday through Friday, from 6 a.m. to 6 p.m. Pacific Time.
Affected students can get two years of free identity protection
ETS is offering affected current and former students 24 months of free identity theft protection. Parents or legal guardians can enroll eligible children under 18, while adults, including former students, can enroll themselves. The services are designed to help monitor for potential identity theft and provide assistance if someone misuses their personal information.
The enrollment deadline is March 19, 2027. Eligible minors who turn 18 before March 19, 2029 may also qualify for adult coverage using the activation code provided in their notification. Enrollment is free, and no credit card is required. Identity restoration assistance is also available to eligible individuals for 24 months from their notification date, even without enrolling in monitoring services. For complete eligibility details and enrollment instructions, visit the California Department of Education's official incident webpage at at cde.ca.gov/nr/in/ets-incident.asp.
How to protect your child after the California student data breach
Even without stolen passwords or financial account numbers, student records deserve serious attention. Here are practical steps I recommend taking if your family may be affected.
1. Verify the breach notification before responding
Scammers frequently use real data breaches as an excuse to send fraudulent emails. A message claiming to come from ETS or Experian could direct you to a fake enrollment website. Instead of clicking an unexpected link, open your browser and visit the official California Department of Education incident page. Follow the verified instructions from there.
2. Consider identity theft protection
Eligible families should take advantage of the 24 months of free identity-protection services being offered following this breach. Follow the enrollment instructions in your official notification and keep a copy for your records. No credit card is required.
For additional protection, consider an identity theft protection service which offers identity monitoring, alerts about suspicious activity and access to restoration specialists if identity theft occurs. Some services also offer paid family plans that can cover children, making it an option for parents concerned about protecting their family's personal information over the long term. Coverage and benefits vary by plan. See my tips and best picks on Best Identity Theft Protection at CyberGuy.com.
3. Consider freezing your child's credit
One of the strongest steps you can take against certain forms of identity theft is placing a security freeze on a child's credit file. The Federal Trade Commission says parents and legal guardians can request a free credit freeze for children under 16. Teenagers ages 16 and 17 can request their own freezes. Contact Equifax, Experian and TransUnion separately. Each bureau has its own process for handling minors. A freeze can make it harder for criminals to open new credit accounts using a child's identity. However, it cannot prevent every form of fraud.
4. Watch for suspicious school-related messages
Pay closer attention to unexpected emails or text messages claiming to involve school records. A scammer with access to personal details could make a fraudulent communication seem unusually credible. For example, someone might claim that your child's testing account requires immediate verification. Before responding, contact the school using a phone number you already trust. Avoid sharing personal information through unexpected links or attachments. Consider using strong antivirus software on your family's devices. It can help detect malicious links, suspicious downloads and malware hidden in fake school notifications. While it cannot recover stolen student information, it adds another layer of protection against scammers who may try to exploit the breach. Get my picks for the best 2026 antivirus protection winners for your Windows, Mac, Android & iOS devices at Cyberguy.com
5. Remove your family's personal information from the internet
Scammers can use information found online to build a more detailed profile of you or your family. That's why I recommend considering a personal data removal service. These services can help remove personal information from data broker websites that collect and sell details such as names, addresses and phone numbers. While these services cannot retrieve information stolen in this breach, they can help reduce how much additional information is publicly available. If you're concerned about your child's information, check whether the service offers protection for minors before signing up. Check out my top picks for data removal services and get a free scan to find out if your personal information is already out on the web by visiting CyberGuy.com.
6. Check for signs of identity theft
Adults who may have been affected can review their credit reports for unfamiliar accounts or suspicious activity. Visit AnnualCreditReport.com to obtain free reports from the three major credit bureaus. Parents should also watch for unexpected bills or collection notices addressed to their children. Those can be warning signs that someone has misused a minor's identity. If you discover evidence of identity theft, report it through IdentityTheft.gov . The FTC provides a recovery plan to help you address fraudulent accounts and document the problem.
7. Ask what information your child's school retains
You can also contact your child's school district to better understand how it handles student records. Ask what information outside contractors receive and how long they retain it. Schools may have legal obligations to maintain certain records. Still, parents can ask about retention policies and security safeguards. This conversation is worthwhile regardless of where your family lives.
Kurt's key takeaways
I've covered plenty of data breaches over the years, but this one bothers me because we're talking about children who had no choice about handing over their information. They went to school, took required tests and trusted the adults and organizations handling their records. Now, some of those details have ended up in the wrong hands. What I find especially troubling is how far back some of these records could go. Think about someone who left California years ago and has no reason to believe their old student information is still sitting on a testing company's system. That person could be living on the opposite side of the country and suddenly have to worry about a breach involving records from childhood. I appreciate that ETS is offering free identity protection, but I'd like to see schools and testing companies explain more clearly how long they keep sensitive student information and why. Parents deserve answers before a breach happens.
Should schools and outside testing companies be allowed to keep sensitive student records for years after a child leaves, or should families have more control over when that information gets deleted? Let us know by writing to us at CyberGuy.com.
Sign up for my FREE CyberGuy Newsletter
Get my best tech tips, urgent security alerts and exclusive deals delivered straight to your inbox.
For simple, real-world ways to spot scams early and stay protected, visit CyberGuy.com – trusted by millions who watch CyberGuy on TV daily.
Plus, you'll get instant access to my Ultimate Scam Survival Guide free when you join.
U.S. Immigration and Customs Enforcement (ICE) has a liaison at the military's Special Operations Command (SOCOM) with access to advanced surveillance technology, leaked files show. The files also reveal ICE liaisons at Africa Command (AFRICOM) and Southern Command (SOUTHCOM) with access to the same tech, and an ICE contractor associated with U.S. Central Command (CENTCOM) in the Middle East.
On Wednesday, a hacker group calling itself the Department of Peace released a massive collection of U.S. Department of Homeland Security (DHS) personnel files, including ICE and other domestic security agencies. "They have our information, so it's only fair that we have theirs," the hackers wrote in a note attached to the database, which was posted online to Distributed Denial of Secrets, a platform for data leaks.
DHS told TheWashington Post that it was "aware of a potential breach" and "working to address the situation swiftly and effectively." A website hosting a searchable version of the leak, ICEpick, was taken down after the DHS sent a letter demanding that the domain name host "stop serving the personal contact and location data of individuals who did not consent."
The files include an ICE Homeland Security Investigations (HSI) unit chief who appears to oversee the agency's military liaisons. His subordinates include a "Combatant Command Program Manager" at SOCOM headquarters in Tampa, Florida; an "HSI Liaison to USAFRICOM" in Stuttgart, Germany; and a "Senior Liaison to U.S. Southern Command" in Doral, Florida.
All of the officials named in the files are listed as users of "Penlink," "Falcon," and "RavenGo." The contractor PenLink offers officials the ability to track individual cell phone users or collect data on everyone in a certain location, according to documents obtained by 404media. FALCON, created by the contractor Palantir, allows officials to combine records from governmental and commercial databases, The Guardianreports. The DHS eventually phased out FALCON in favor of an in-house system, RAVEN.
The unit chief is additionally listed in a group called "LCR_Users." The acronym may refer to the Office of the Director of National Intelligence at Liberty Crossing, McLean, Virginia. Two employees are listed in the DHS files with "ODNI" in their title and "LCR - Liberty Crossing" as their location. The first Trump administration reportedly looked into merging ICE into the federal intelligence community, but never officially did so.
The files also include an HSI contractor listed as "CENTCOM analyst" at the National Targeting Center in Sterling, Virginia. Unlike the other liaisons, this contractor does not have access to ICE's own surveillance software. The National Targeting Center is a Customs and Border Protection (CBP) unit that surveils international travel and selects passengers for questioning. CENTCOM oversees all U.S. military forces in the Middle East.
Although it has been mentioned in public, ICE's relationship with the military is shrouded in mystery. Of course, the best-documented relationship is with SOUTHCOM, responsible for U.S. forces in Latin America. Official press releases also mentioned HSI's participation in an AFRICOM maritime security training exercise in 2021. The connections to SOCOM and CENTCOM have not been publicly reported.
ICE did not respond to Reason's request for comment.
The DHS has an in-house intelligence office that is separate from HSI and publicly cooperates with the U.S. military, as well as the rest of the intelligence community. But HSI's "global footprint" and ability to straddle the line between law enforcement and foreign policy "make it uniquely capable of disrupting and dismantling the sophisticated groups and networks that we now face," HSI Executive Assistant Director Katrina W. Berger testified to Congress in 2024.
HSI is supposed to handle serious organized crimes involving the border rather than day-to-day deportations. However, the Trump administration has turned the directorate into an all-purpose domestic spying and enforcement arm. HSI is now running a massive surveillance operation against left-wing protesters, WIRED recently revealed.
Agents have reportedly been pulled away from investigating human trafficking and drug cartels to deal with immigration enforcement. HSI was involved in arresting former CNN journalist Don Lemon for showing up at an anti-ICE protest at a church, and led the raid against Rep. Ilhan Omar (D–Minn.) reportedly aimed at showing that her U.S. citizenship is invalid.
Last month, ICE announced upcoming contracts for a $100 million, fast-tracked expansion of its domestic surveillance capabilities, with contractors asked "to identify and assess relationships among individuals, organizations, locations, events, activities, data points, and other entities." Former military intelligence analyst Michael Wriston called the intensified ICE surveillance a case of "imperial boomerang" in an interview with The American Prospect. "These are the kinds of things that happened in Afghanistan, Iraq, Yemen, Syria, for years. Now that methodology is being brought into the ICE space."
Russian hostile activity costs the UK at least £2 billion (US$2.7 billion) annually, according to a recent report by Scottish MP Graeme Downie, who has called on the government to measure what these actions cost Britain. But this figure is just the baseline. In reality, a profound shift in Moscow’s approach to sabotage means the […]
If you're reading this, then the internet still works. But that's something that we shouldn't necessarily take for granted after this week's global cybersecurity meltdown.
"Think of it this way: someone discovered that millions of buildings in the country have the same broken lock, and now everyone knows how to open it," writes Matt Shumer in a lengthy post on X about the situation. "The lock maker has sent out a fix, but every building owner has to install it themselves, and many haven't yet."
This is the world we live in now. In August, more than 100 tech companies signed a letter warning about exactly this possibility. On Thursday, one of Anthropic's top information security officers wrote that cybersecurity threats "are going to get a lot worse before they get better." Major banks are rushing to secure themselves after reports of autonomous agents operating inside accounts (though many of them may have been authorized by account holders).
This is unlikely to be the last incident like this. Cybersecurity firm CrowdStrike says it saw twice as many "agentic intrusions" (hacking done by an autonomous or semiautonomous AI) in August as in July, and then the number doubled again in September.
Scary stuff, for sure. As is usually the case, however, prevention is better than panic.
Shumer's post contains many helpful suggestions for better online security—it is particularly important to secure your email accounts, since that is the gateway to so much of what we do online. Here's a 15-step plan to stay more digitally secure in the AI age. (And if you're really worried about everything falling to bits, Reason's got you covered there too.) If your devices and browsers have updates available, install them. And for the love of digital gods, don't click on random links in strange emails!
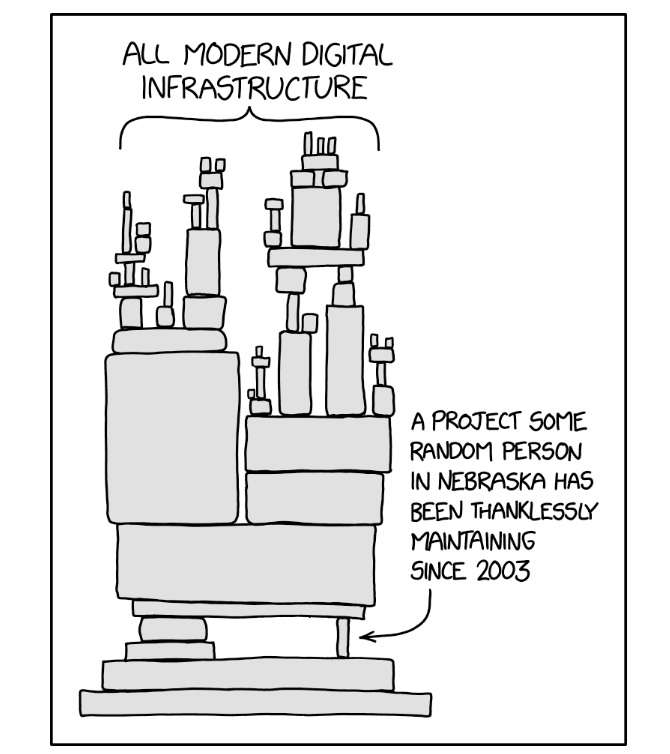
The man who (maybe) saved the internet? There is an old XKCD webcomic—and I'm dating myself as a very specific type of millennial by even referencing that—that seems to perfectly sum up what happened this week. Here it is:
Source: https://xkcd.com/2347
Here's the craziest part: That's basically true! Except the one random person lives in Czechia instead of Nebraska. His name is Ondřej Surý, and TheAtlantic's Charlie Warzel found him:
Surý, who lives in Czechia, does not work for the PHP Foundation. But alongside his day job as director of domain-name-system engineering at the nonprofit Internet Systems Consortium, in a volunteer capacity, he maintains and helps automate patches for the coding language. His work, with that of just a handful of others, has allowed countless websites and organizations to fix these vulnerabilities quickly. Over the past 48 hours, he's become arguably the unsung hero of the entire internet—despite the fact that the only compensation he receives is from modest donations. "Ondřej will save the internet today," a user in the PHP Subreddit wrote.
In the war between AI hackers and AI defenders, it's still humans who are the heroes. At least for now.
Art of the steal. Yesterday, in this space, I detailed how voters are fed up with the Trump administration's seemingly endless stream of corruption. But it's been a whole 24 hours, which means there is yet another scandal in the news—thanks to a Vanity Fairarticle about President Donald Trump's son-in-law Jared Kushner.
The article is an excerpt from a forthcoming book. In it, author Matthew Cole claims that Dutch investigators gained access to Kushner's phone with the help of Russian hackers. The evidence from the phone and other sources shows that Kushner has been taking money from the governments of Saudi Arabia and the United Arab Emirates to "push their agenda with Trump."
Kushner says the article's claims are "outrageous and categorically false."
But wait, there's yet another corruption story. The Justice Department is reportedly probing whether Trump ally Corey Lewandowski profited from his role as a top adviser at the Department of Homeland Security (DHS). The Washington Post reports that the investigation is based on a referral from the DHS inspector general and is focused on "contracting fraud."
It may or may not be connected to other allegations that surfaced in September, when The Wall Street Journalreported that Lewandowski approached officials in Qatar and the UAE about being hired to help with "visa issues" and other matters.
In both matters, Lewandowski has denied the allegations. He's no longer working for the department, having been fired earlier this yearamid a messy scandal involving then–DHS Secretary Kristi Noem, who was also canned.
Scenes from Virginia: Federal prosecutors indicted state Sen. L. Louise Lucas (D–Portsmouth), one of the most powerful Democrats in Virginia, on charges of racketeering and money laundering in connection with illegal marijuana sales. (Don't get me started on how dumb it is that recreational marijuana use has been legal here since 2021, but commercial sales are still forbidden. If it's legal to use something, it should be legal to sell it!)
Lucas pushed the failed Virginia redistricting effort and has been an outspoken critic of Trump. She plans to fight the charges. Virginia Gov. Abigail Spanberger, also a Democrat, said in a statement that the timing of the indictment, just days before the midterm elections, "further erodes the trust the American people deserve to have in the Department of Justice."
QUICK HITS
"The last thing José García-Sorto remembers after being shot in the chest is being pulled from his car, pinned to the pavement and handcuffed, his blood pooling around him on a Phoenix interstate. All he could think about was what would happen to his two young children if he died." The New York Times has a harrowing account of a Honduran immigrant who was shot by immigration officers last year. He's never been charged with a crime in connection with the incident, which suggests "the authorities did not find evidence that he had put anyone in danger."
The Cato Institute's annual ranking of "Freedom in the 50 States" is out. Arizona takes the top spot. How did your state do?
Is alchemy real now? A California company claims it has successfully turned mercury into gold.
The World Series begins tonight, and it ought to be terrific. Despite low payrolls, Tampa Bay and Milwaukee were the top teams in their respective leagues this year. They are deep, talented teams full of characters worth cheering—Brewers' star pitcher Jacob Misiorowski is a huge Pokémon nerd; Rays' star hitter Yandy Diaz escaped from Cuba after being imprisoned there. And this is the first World Series since 1980 to match two franchises that have never won a championship.
An uncanny strength of the second Trump administration has been its ability to be involved in so many scandals that no single one seems to become a dominant story.
Take the most recent allegations about Alina Habba, Trump's former personal defense attorney, who recently landed a plush gig working for Julio Herrera Velutini, a Venezuelan banker. Habba will get $50 million over five years to do unspecified work for a company that barely exists, according toThe New York Times, while Herrera got a presidential pardon for a 2025 campaign finance charge.
But that constellation of corruption might finally be breaking through to voters ahead of next month's midterm elections.
A recent Fox News poll found that "government corruption" was the top issue for voters, ranking ahead of inflation and gas prices. Conservative commentators are taking notice.
"What they're saying is, 'Look, we're tired of you getting rich and us getting poor,'" former White House Chief of Staff Mick Mulvaney said this week.
Tim Carney, senior columnist at the conservative Washington Examiner, also tabs the corruption issue—along with other "avoidable mistakes" such as the Iran War and tariffs—as one of the major reasons why Democrats are likely to win the midterms:
Trump and his family have enriched themselves in this second term in ways more similar to third-world regimes or Cook County than to any previous administration. He and his family operate a financial company that has received heavy investments from Qatar's government. He's sold access to himself by selling otherwise worthless cryptocurrency. The IRS he controls settled a lawsuit with him, promising to pay him $1.8 billion (this settlement was voided by a judge).
Trump is not directly on the ballot next month, of course. And most voters might not be able to tell you the details of any single Trump scandal in detail. Even so, this may turn out to be the defining narrative of the second Trump administration, and there seems to be a growing consensus that Republicans have allowed (if not aided and abetted) his corrupt behavior, so it's time to give Democrats a shot at reining it in.
The Trump corruption issue is like the Biden cognitive decline issue in one key sense: Everyone around the president or even supporting him professionally from afar should be asked about it, and their lies/claims of ignorance should be hung around their necks like dumbbells.
Vice President J.D. Vance told journalist Mark Halperin this week that he's "never seen any evidence that anybody's selling access to the president." When Halperin pushed back, Vance doubled down: "What I would say is I don't think there's evidence that the Trump family has become enriched by politics," the vice president said.
So either Vance isn't paying attention, or he's deliberately misleading. "Credit to Vance, it's as good an argument as is available to him," writes Daniel Foster at National Review. "The bad news is it's still not very good."
The internet nearly crashed on Wednesday as digital security and website administrators scrambled to patch two vulnerabilities in the PHP programming language that serves as the basis for many websites.
"Since its development in the 1990s, PHP has evolved into an essential scripting language for web development and is used across vast swaths of the internet in websites and software," explainsWired. "Everything from publishing systems like WordPress and Drupal to e-commerce platforms like Adobe's Magento are built on PHP."
The potential hacking abilities of advanced AI agents make these sorts of security risks more serious. In this case, however, the problem was also identified with the help of AI.
"Ryan Austin, a researcher at Calif, uncovered the flaws with help from GPT-5.6 Sol, one of OpenAI's most advanced models, during an audit of PHP's source code in August," The Wall Street Journalreports. Another security researcher had flagged the issue years ago, but it had never been fixed because it was considered "considered too difficult to exploit" by human hackers.
This is the future of humanity's digital landscape. "Given the severity of these flaws and PHP's widespread use, we consider this one of the most impactful security issues in recent memory," OpenAI said in a statement on Wednesday. "It highlights how AI can uncover security flaws with internet-scale impact, but the same capabilities can also help attackers rapidly develop offensive tools and exploits."
(A shoutout to Reason's web development team for keeping us up and running, today and every day.)
"Fanciful fiction." Media outlets also continue to face decidedly nondigital threats over articles and polls that make the president unhappy.
The White House threatened Politico on Wednesday with unspecified "consequences" for publishing "fanciful fiction" in a series of articles earlier this month about White House Chief of Staff Susie Wiles. If the articles are not retracted, it would trigger "an immediate review of Politico's relationship with the White House, and, of course, consideration of all other appropriate and available legal remedies," wrote White House counsel William O. Scharf in a letter to the media outlet's publisher.
Meanwhile, FCC Chairman Brendan Carr issued vague threats to broadcasters who cover what Carr called "Fake Polls" intended to "alter the normal patterns of voter turnout and enthusiasm."
These sorts of threats are an affront to the First Amendment, of course. But they are downstream of a more significant issue: the very existence of the FCC.
It's a problem, obviously, that the FCC is run by an authoritarian jackass. But the bigger problem is that the agency contains so many tempting tools for an authoritarian jackass to wield. https://t.co/Q4IJXntkOy
A judge in New Mexico ordered social media giant Meta (which owns Facebook and Instagram, among other things) to pay $25 billion for misleading users about data privacy. Last month, a jury found that Meta had violated the state's consumer protection laws 43 million times.
The environmental studies for California's high-speed rail line include such absurdities as counting bumblebees "one by one" and considering the train's "acoustic impacts on waterfowl and shorebirds." That's how to spend 16 years and $15 billion building nearly nothing.
Obvious metaphor alert!
A group dispatched by Hegseth's team in February attempted to move the historic globe, said to be used by Eisenhower during World War II.
They lifted it from its home in an Army office in the Pentagon … and dropped it. pic.twitter.com/vTjWdYXn0k
Prime Minister Rob Jetten of the Netherlands in Brussels last week. He said that his cabinet was closely monitoring the online vulnerability caused by a security flaw in PHP.
The website for the French government was temporarily unavailable on Wednesday amid hacking concerns stemming from major bugs in a piece of software used widely across the internet.
 Login