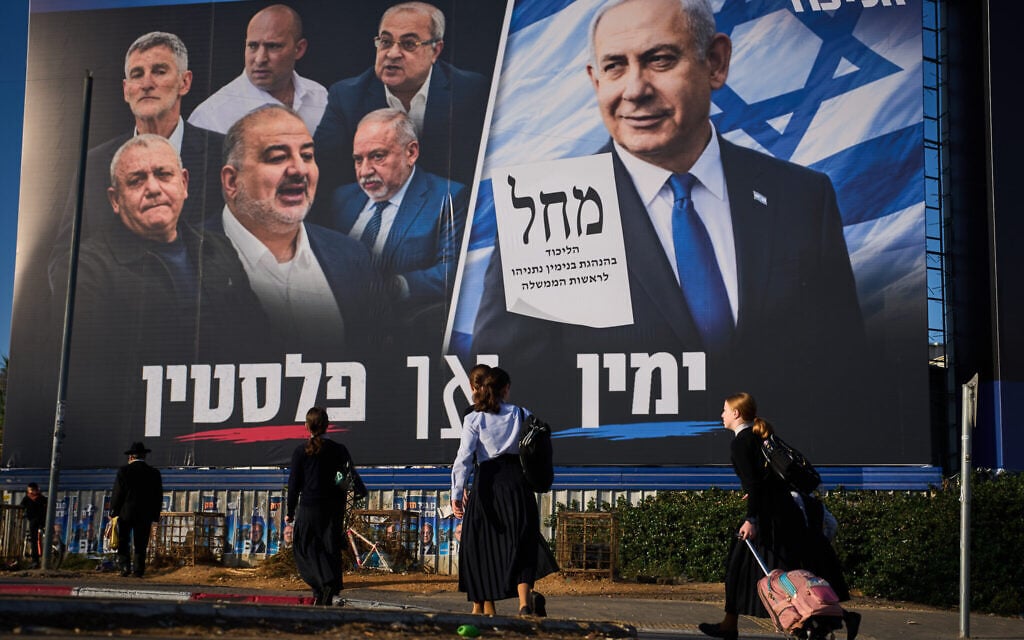
There’s already violence in the streets, candidates are receiving death threats and a specter of war looms over the country. And that’s before any ballots have been counted
France, Germany, Austria and Poland are expanding or reviewing the authority of critical infrastructure operators to defend facilities against drones, raising legal and operational questions over the growing role of civilian companies in national security.
European governments are reconsidering who should be authorised to intercept hostile drones as energy companies and critical infrastructure operators confront an increasingly serious threat to electricity networks, transport systems and other essential facilities.
France has already introduced legislation permitting approved operators to deploy counter-drone systems, while Germany is reviewing similar arrangements and Austria has announced plans to extend certain protective powers to infrastructure companies.
Poland has moved further by authorising designated security units to disable or destroy drones entering restricted areas around important energy installations.
The changes reflect concerns that national police and armed forces cannot provide permanent protection for every substation, power station, railway facility or pipeline against relatively inexpensive unmanned aircraft.
France establishes a new approach
In August 2026, the French parliament approved legislation allowing authorised operators of critical infrastructure and their contractors to detect, jam and intercept drones near designated facilities.
The legislation followed a series of reported drone incursions over sensitive locations, including military installations.
Under the French approach, operators of strategically important infrastructure may eventually use approved counter-drone systems without relying exclusively on the immediate intervention of military personnel.
Potential beneficiaries include electricity operators and organisations responsible for transport infrastructure.
French authorities are testing detection equipment, electronic countermeasures and interceptor drones at Brétigny-sur-Orge, south of Paris.
The programme examines systems capable of identifying approaching aircraft, determining whether they present a threat and initiating an appropriate response.
France intends to expand the protection of sites classified as strategically important, with further deployment planned during 2027.
The initiative would introduce responsibilities traditionally associated with military or police operations into the management of civilian infrastructure.
Germany and Austria reconsider existing restrictions
Germany is examining the legal conditions under which private companies and infrastructure operators could participate in active counter-drone operations.
At present, responsibility for neutralising threatening aircraft remains primarily with the competent public authorities.
The debate has intensified following security incidents involving unmanned aircraft, including the discovery of an explosives-laden drone near a Ukrainian cargo aircraft at Leipzig/Halle airport in August.
German authorities attributed the incident to Russia, an allegation Moscow denied.
The German government’s review concerns not only the equipment that companies may possess but also whether trained security personnel should be permitted to deploy countermeasures without waiting for a separate police authorisation.
Austria announced plans in September to extend comparable powers to selected critical infrastructure operators, including major energy companies.
The government has acknowledged the practical limitations of protecting a large number of widely dispersed installations using state security personnel alone.
Poland has already established restricted drone zones around sensitive energy facilities, with designated security units authorised to intercept aircraft entering those areas under applicable national rules.
Electricity networks face particular risks
Electricity infrastructure presents a difficult security problem because essential installations are distributed across extensive geographical areas.
Transmission operators manage thousands of kilometres of high-voltage lines, while substations, transformers and switching stations connect generation facilities to consumers.
A successful attack against critical equipment can produce consequences extending well beyond the immediate site.
Large power transformers are particularly difficult to replace. Manufacturing, transporting and installing specialised equipment can require lengthy preparation, making rapid recovery uncertain after serious damage.
European utilities have traditionally concentrated on physical security, maintenance and restoring services after technical failures or accidents.
The spread of drones creates additional demands for surveillance, early warning and the ability to respond before an attack reaches its target.
Russia’s repeated strikes against Ukraine’s electricity infrastructure have demonstrated the extensive disruption that attacks on power systems can cause.
European governments are now evaluating how comparable vulnerabilities could be exploited against their own networks.
Electronic jamming can interfere with communications and navigation systems beyond the targeted aircraft. A drone brought down over an industrial or residential area could injure members of the public or damage surrounding property.
Security personnel must also determine whether an unidentified drone is hostile, operating unlawfully or simply present because of an error by its operator.
A mistaken interception could expose infrastructure companies to compensation claims and other legal consequences.
European governments must therefore establish who can authorise an intervention, which countermeasures are permitted and how responsibility is allocated when damage occurs.
There is no uniform European approach.
Some operators support expanding their protective powers, while others argue that the use of force should remain the responsibility of the state.
Finland’s national electricity transmission operator, Fingrid, has expressed reservations about transferring such authority to energy companies.
The position reflects a wider concern that infrastructure operators should concentrate on maintaining essential services rather than assuming responsibilities for armed or coercive security operations.
A growing European security market
The regulatory debate is developing alongside a rapidly expanding market for counter-drone technology.
Manufacturers are offering equipment that integrates radar, optical sensors, electronic detection and software capable of classifying possible threats.
Interceptor drones and electronic countermeasures are increasingly being designed for use around civilian infrastructure rather than exclusively on military installations.
German defence company Rheinmetall has reported growing interest from private infrastructure operators in counter-drone protection.
However, the technology is advancing faster than the legal frameworks governing its use.
The immediate challenge for European governments is to establish protective arrangements that allow rapid intervention while preserving clear accountability.
A counter-drone system can identify an approaching aircraft within seconds. Determining who is authorised to stop it remains a matter for national law.
Latvia has called for a European Union-wide ban on tourist visas for Russian citizens, reopening a dispute between member states over border security, freedom of movement and the treatment of Russian nationals during Moscow’s continuing war against Ukraine.
Prime Minister Andris Kulbergs is pressing Brussels and other European capitals to adopt a common approach, arguing that continued visa issuance by some Schengen countries weakens restrictions imposed by states bordering Russia.
His intervention comes amid growing concerns over suspected Russian sabotage, espionage and other hostile activities across Europe. The Latvian government regards restrictions on non-essential travel as an additional measure to reduce potential security risks.
According to details of the Latvian proposal, Kulbergs has criticised the continued issuance of tourist visas by countries including France, Italy and Spain, maintaining that the consequences extend beyond the states granting entry.
The proposal would go considerably further than the restrictions already introduced by the EU since Russia launched its full-scale invasion of Ukraine in February 2022.
A divided European visa policy
The European Union suspended its visa facilitation agreement with Russia in September 2022, ending the preferential conditions previously available to Russian applicants.
The Council’s original decision introduced more demanding documentation requirements, higher application fees and stricter scrutiny, but it did not prohibit Russian citizens from obtaining short-stay visas.
National authorities therefore retained considerable discretion when assessing applications, subject to common Schengen rules.
The EU has also agreed a legal basis for restrictions targeting Russian military personnel and former combatants involved in the invasion of Ukraine, although implementation requires further measures.
Latvia argues that these steps remain insufficient because ordinary tourist visas continue to be available through some European consulates.
Once admitted to the Schengen area, a visitor can generally travel between participating countries without routine internal border checks. This creates difficulties for governments seeking to enforce stricter national entry policies.
Security concerns on the eastern border
Latvia shares borders with Russia and Belarus and has repeatedly warned that Moscow’s activities present risks extending beyond conventional military threats.
European governments have investigated incidents involving suspected sabotage, cyber operations, intelligence gathering and interference with transport infrastructure.
Such concerns have intensified following drone incursions and security alerts affecting NATO’s eastern members.
The distinction is relevant to the Latvian proposal. European intelligence agencies have identified Russian-linked activities, but this does not establish that ordinary Russian tourists are collectively involved in intelligence operations.
Supporters of tighter visa restrictions argue that limiting discretionary entry could reduce opportunities for hostile activity and simplify security screening.
Opponents question whether a nationality-based prohibition would be proportionate or effective, particularly when intelligence operations may involve individuals travelling under other nationalities or using established residency arrangements.
Political and legal complications
A comprehensive tourist visa ban would require agreement on its precise scope, legal basis and implementation.
European governments would need to determine how the restrictions apply to Russian citizens with family members in the EU, people travelling for humanitarian purposes and individuals seeking protection from the Russian authorities.
The EU Visa Code already permits refusals where applicants present security risks, but a general prohibition based on nationality would involve a different policy decision.
Humanitarian exceptions would be particularly important for Russian dissidents, independent journalists and other individuals facing political persecution.
France has supported restrictions on entry by Russian combatants, while other member states are considering further measures. That does not necessarily mean they support Latvia’s broader proposal covering ordinary tourists.
Kulbergs is also seeking greater European financial assistance for countries facing the economic and security consequences of their proximity to Russia and Belarus.
Sanctions and Schengen controls
The renewed visa debate coincides with disagreements between Washington and Brussels over economic restrictions on Moscow.
EU leaders have maintained that sanctions should remain in place until Russia ends its aggression against Ukraine. Visa policy, however, requires separate legal and political consideration from economic sanctions.
Latvia’s proposal has not been adopted as an EU-wide rule. The immediate question is whether enough member states are prepared to move from tighter individual screening towards a general restriction on Russian leisure travel.
Until that agreement is reached, European countries will continue to apply different policies within a shared Schengen system, leaving the security concerns raised by Riga unresolved.
An apparent vehicle breach at Leipzig/Halle Airport has renewed questions about infrastructure protection. After an earlier drone incident blamed on Russia, Germany faces the challenge of responding firmly while allowing evidence to determine responsibility.
A damaged airport fence would ordinarily be a local policing story. At Leipzig/Halle, it carries a heavier significance. Following an attempted drone attack earlier this year, another security incident inevitably raises questions about whether Germany can adequately protect infrastructure operating in an increasingly hostile environment.
Yet the central distinction remains essential: an apparent perimeter breach is under investigation. Its cause, purpose and perpetrators have not been established. The implications deserve scrutiny; suggestions of another foreign operation remain speculation.
Police said damage was discovered shortly before 11pm on Saturday, October 17th. The northern runway was closed while federal and state officers searched the grounds. In a Sunday morning update, investigators said a vehicle had most probably broken through the fence. Initial searches found neither unauthorised people nor suspicious objects, with further searches planned.
Those findings provide reassurance without resolving the incident. Investigators still need to establish how the damage occurred, whether anyone entered restricted areas and whether the apparent breach was deliberate. Until those questions are answered, describing it as sabotage would run ahead of the evidence.
The operational picture also requires proportion. Although the northern runway remained closed, airport spokesman Uwe Schuhart said on Sunday morning that passenger and freight flights were continuing without restrictions because the second runway remained available. This was a significant security response, but not an airport-wide shutdown.
That distinction matters politically. Public confidence depends on authorities explaining both the seriousness of a suspected intrusion and the effectiveness of arrangements that keep essential services functioning.
Leipzig’s recent history nevertheless makes heightened vigilance understandable. Reuters recalled that investigators discovered an explosive-laden drone near a runway in August. German officials subsequently attributed responsibility to Russia, which denied the allegations. No connection between that episode and the latest fence damage has been established.
The earlier incident changes the context in which airport authorities must make decisions. Once a location has faced a potentially lethal threat, uncertainty becomes more expensive. An unexplained opening in a perimeter cannot be treated casually simply because the first search produces nothing suspicious.
This creates an uncomfortable imbalance. Damage that takes little time to inflict can require extensive searches, specialist personnel and precautionary closures. Whether caused by criminality, recklessness or hostile intent, a breach can impose costs far beyond the price of repairing a fence.
The wider German security debate gives those concerns additional weight. On October 12, Reuters reported warnings from Interior Minister Alexander Dobrindt about a “shadow war”. Domestic intelligence chief Sinan Selen described Russian activities encompassing disinformation, sabotage and assassination preparations, and said he expected further incidents resembling the earlier Leipzig drone episode.
Those warnings justify preparedness. They do not establish who damaged this fence. Conflating the two would weaken public understanding and risk turning every unexplained incident into an assumed act of geopolitical aggression.
For policymakers, the practical questions are more useful than premature attribution. How quickly was the damage detected? Could security personnel reconstruct movements around the affected area? Were protective measures proportionate to the risks? And what improvements, if any, would reduce the interval between a breach and a reliable assessment?
The airport’s continued operation offers one encouraging lesson: resilience includes maintaining service while investigating danger. A second runway provided operational flexibility. Similar thinking should guide investment across critical infrastructure, where preventing every disruption may be impossible but limiting its consequences remains achievable.
There is also a clear accountability test. Once investigators establish what happened, authorities should explain the findings and any resulting changes without revealing details that would assist future intruders. An accident, an ordinary crime and a hostile operation would demand different responses.
For now, Leipzig presents a warning about vulnerability rather than proof of another attack. Germany needs the capacity to investigate rapidly, protect exposed facilities and sustain normal life under pressure. Its credibility will depend on demonstrating those capabilities—and maintaining the discipline to distinguish justified suspicion from established fact.
Poland has launched a nationwide security operation after three knife attacks at educational institutions left one woman dead and more than a dozen people injured. Police have detained 117 people amid a wave of online threats, while intelligence officials are examining whether Russian disinformation networks exploited the violence to spread panic.
Poland is confronting an unprecedented school security crisis after a succession of violent attacks by young people triggered widespread fear, school closures and a nationwide police mobilisation. By Sunday, 11 October, officers had detained 117 people and conducted nearly 64,000 security checks at educational establishments, as the authorities attempted to contain both genuine threats and an escalating campaign of intimidation on social media.
The crisis reached its height on Friday, 9 October, when warnings circulated about a supposed nationwide killing campaign known as “Bloody Friday”. Videos, threatening messages and lists of potential targets spread through TikTok, messaging platforms and school discussion groups, prompting parents to keep children at home and several local authorities to suspend classroom teaching.
Although police have found no evidence of an organised nationwide conspiracy, the violence that preceded the rumours was real. Three separate attacks took place between 7 and 10 October, while investigators are examining hundreds of other incidents involving threats or suspected criminal activity.
Two attacks that triggered nationwide panic
The first major incident occurred on Wednesday, 7 October, at a vocational school in Ostrołęka, north-east of Warsaw. A 19-year-old student armed with a machete attacked pupils, teachers and other people in and around the building, injuring nine victims before harming himself.
Investigators subsequently discovered a homemade explosive device inside his backpack. The suspect was arrested, and prosecutors brought nine charges against him, including attempted murder. The discovery of explosives raised further questions about the extent of his preparations and the possibility of a substantially higher death toll.
The following day, a 15-year-old former pupil entered a primary school in Leszczydół-Nowiny, near Wyszków, and attacked three members of staff with a knife. A 37-year-old caretaker died from her injuries, while two teachers, including the headteacher, were wounded.
According to investigators, the teenager wore a helmet-mounted camera, raising suspicions that he intended to record the assault. The official prosecution statement confirmed the victim’s death and the detention of the suspect.
The attacks were followed by threatening messages from other teenagers, including a video attributed to a 17-year-old in the Przasnysz district who claimed to be participating in a competition involving killings. Police subsequently detained him. In Sierpc, another 17-year-old was arrested after allegedly discussing plans for violence at school; officers discovered two knives.
Thousands of schools under police surveillance
The rumours produced an immediate reaction. Schools in Wyszków, Ciechanów, Pułtusk and other municipalities cancelled classroom teaching or introduced remote lessons. Elsewhere, parents independently withdrew their children, leaving some classrooms largely empty.
Police launched an extensive preventive operation, deploying additional officers around schools and investigating online threats.
According to the figures released on 11 October, the authorities had recorded 275 incidents requiring investigation, detained 117 people and carried out nearly 64,000 checks at schools, nurseries and other educational facilities.
The situation deteriorated further on Saturday, 10 October, when a 21-year-old student attacked three people at a post-secondary educational institution in Warsaw. Two 17-year-old girls and a 24-year-old woman were injured. One victim required hospital treatment, although none of the injuries was considered life-threatening.
Interior Minister Marcin Kierwiński subsequently stated that investigators had established no links between the recent attacks. The authorities nevertheless remain concerned about imitation offences, particularly where threatening material circulates among teenagers through closed online communities.
Russia’s possible role in spreading panic
The events have also raised questions about whether hostile foreign actors deliberately amplified the crisis. Tomasz Siemoniak, Poland’s minister responsible for coordinating the intelligence services, warned that Russian organisations routinely exploit domestic emergencies to spread disinformation and undermine confidence in public institutions.
In his statement on 9 October, Siemoniak acknowledged the possibility of foreign involvement but stressed the need for evidence before assigning responsibility.
There is, at present, no publicly established evidence that Moscow organised the school attacks or directed the subsequent threats. Nevertheless, the rapid circulation of alarming videos, fabricated warnings and unverified target lists illustrates how genuine violent incidents can be exploited to disrupt everyday life without further physical attacks.
The episode also presents a challenge for European regulators. Poland is examining measures against dangerous online content, while its existing obligations under the EU Digital Services Act provide a framework for addressing systemic risks associated with major platforms.
For Donald Tusk’s government, the immediate priority is preventing further attacks as schools reopen under heightened security. The longer-term challenge concerns the interaction between online radicalisation, copycat violence and disinformation capable of transforming isolated crimes into a national emergency.
Several bomb threats by anonymous callers targeting diplomatic missions and commerce buildings in central Athens triggered a major police response Friday morning. Authorities have been carrying out security checks at four locations, including the French Consulate, the Egyptian Embassy and two business organizations. According to Greek Police, unknown callers contacted the French Consulate and the […]
 Login